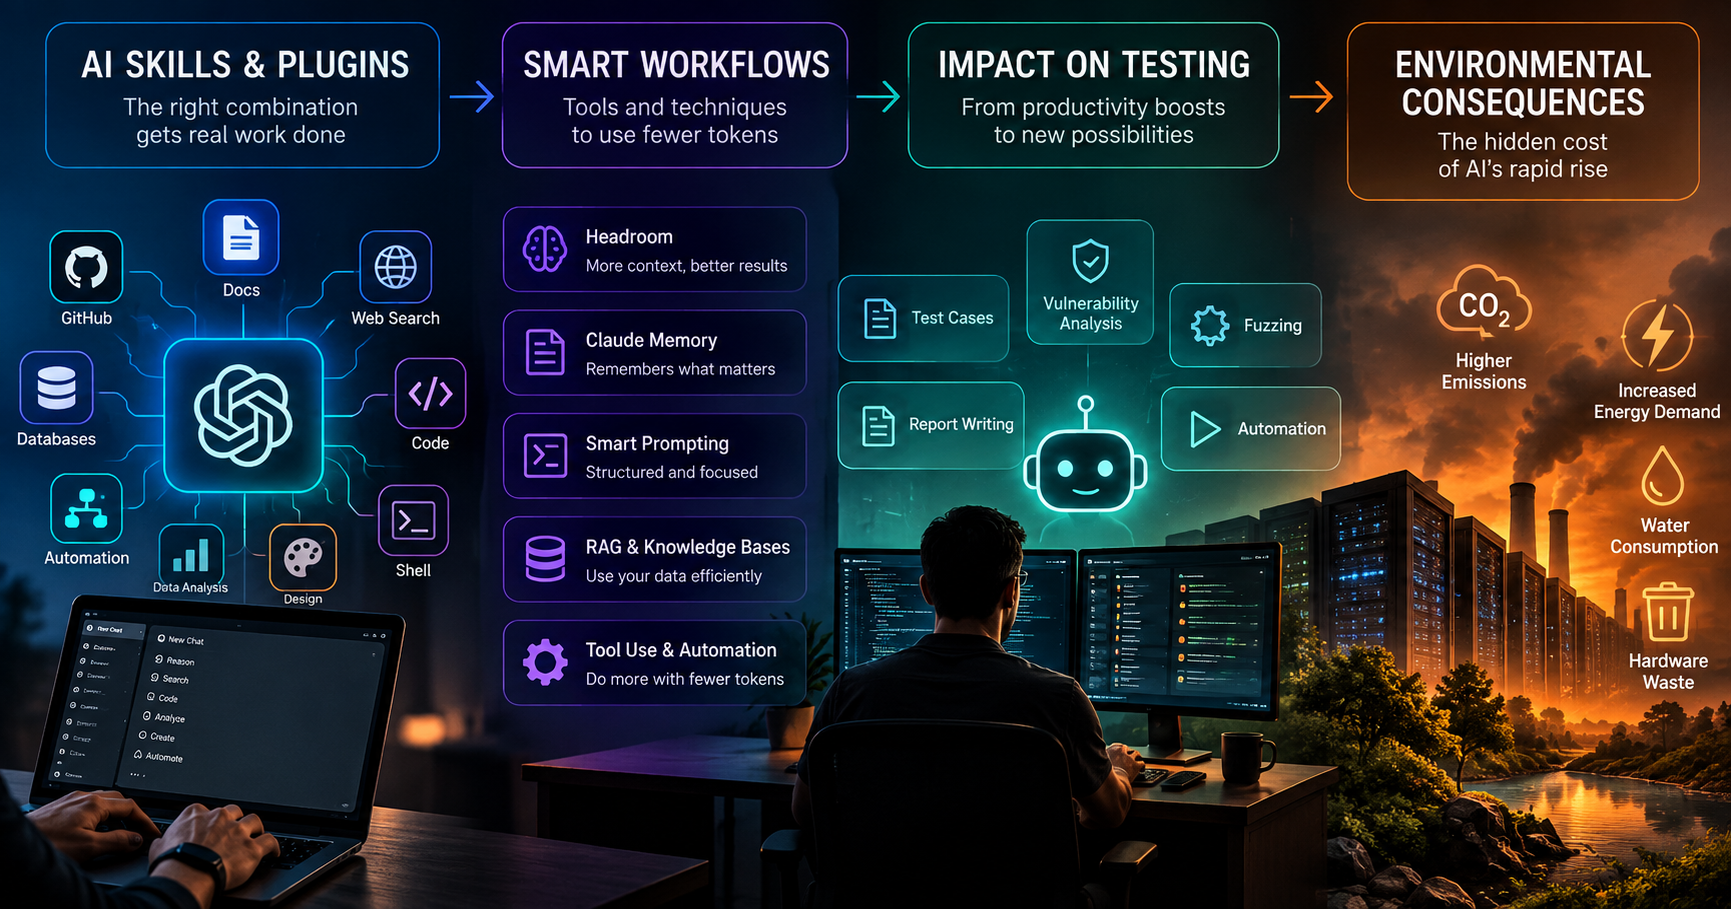
How AI Is Changing Software Testing and VAPT
How AI is moving from test assistance toward agentic testing, changing test generation, automation, defect analysis, security testing, and the role of the tester.
$ whoami
Security Engineer · Penetration Tester · Risk Advisor
I secure web applications, APIs, mobile applications, and networks by identifying vulnerabilities before attackers can exploit them. I also lead security teams, drive technical delivery, advise on cybersecurity and risk, and help organizations strengthen their security posture through effective people, processes, and technology.
Modular reconnaissance and vulnerability-scanning framework with a PyQt5 GUI. Plugin-based tool integration, parallel scanning, custom scan profiles, dashboards and an interactive CVSS v3.1 calculator.
Frida-based SSL/TLS pinning bypass framework for Android. Hooks TrustManager, HostnameVerifier and related trust mechanisms at runtime to enable HTTPS interception without repackaging the APK.
Subdomain Finder & Accessibility Checker. Enumerates subdomains via Sublist3r, checks which are live, captures headless screenshots and exports results to CSV.
How AI is moving from test assistance toward agentic testing, changing test generation, automation, defect analysis, security testing, and the role of the tester.
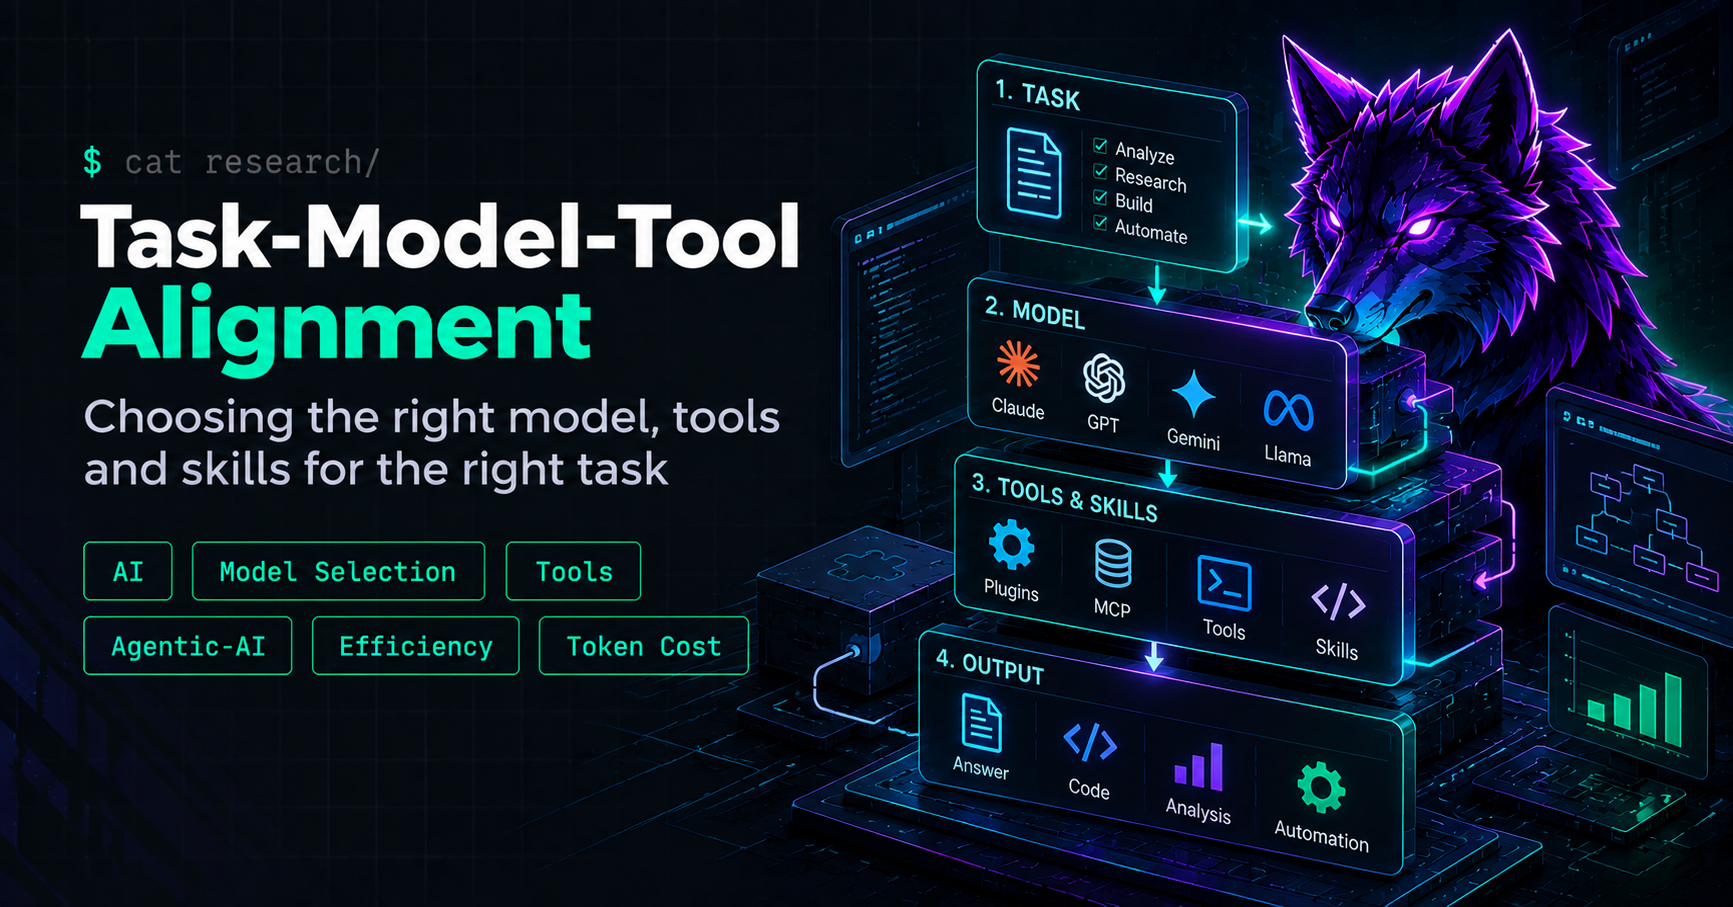
Why AI efficiency depends on task-model-tool alignment and total token cost rather than simply adding more models, tools, and skills.
The environmental consequences of rapidly growing AI workloads, including electricity demand, water consumption, carbon emissions, hardware manufacturing, and the efficiency-versus-scale paradox.
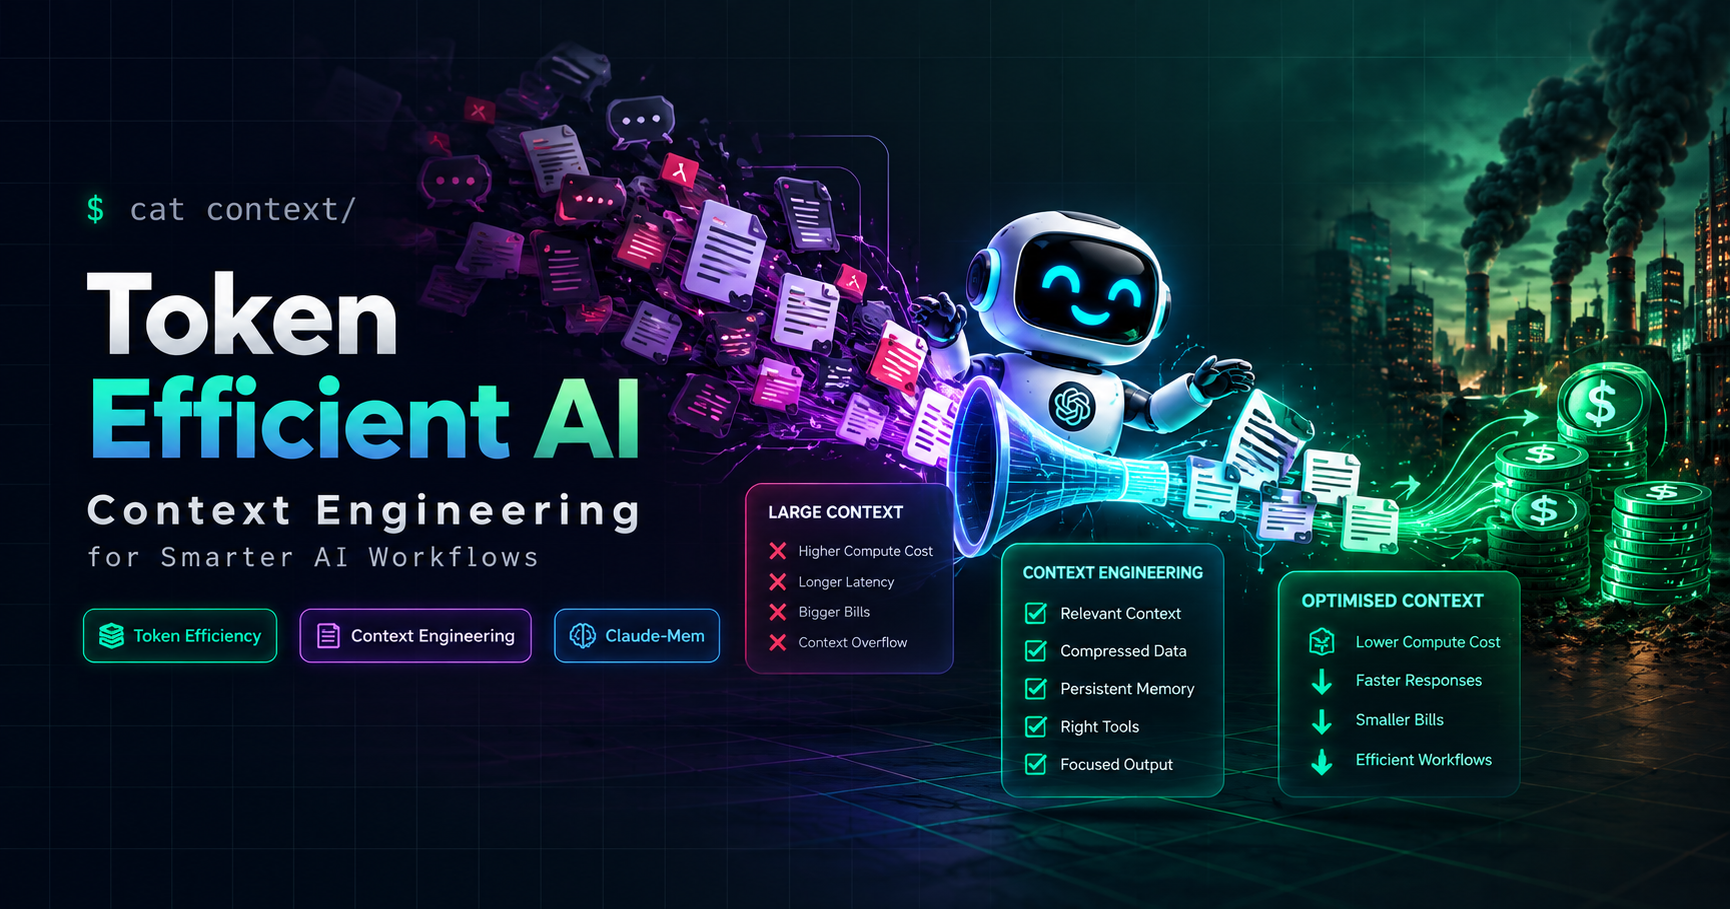
How context compression, progressive disclosure, persistent memory, subagents, dynamic tool loading, and efficient context design reduce unnecessary AI computation and context consumption.
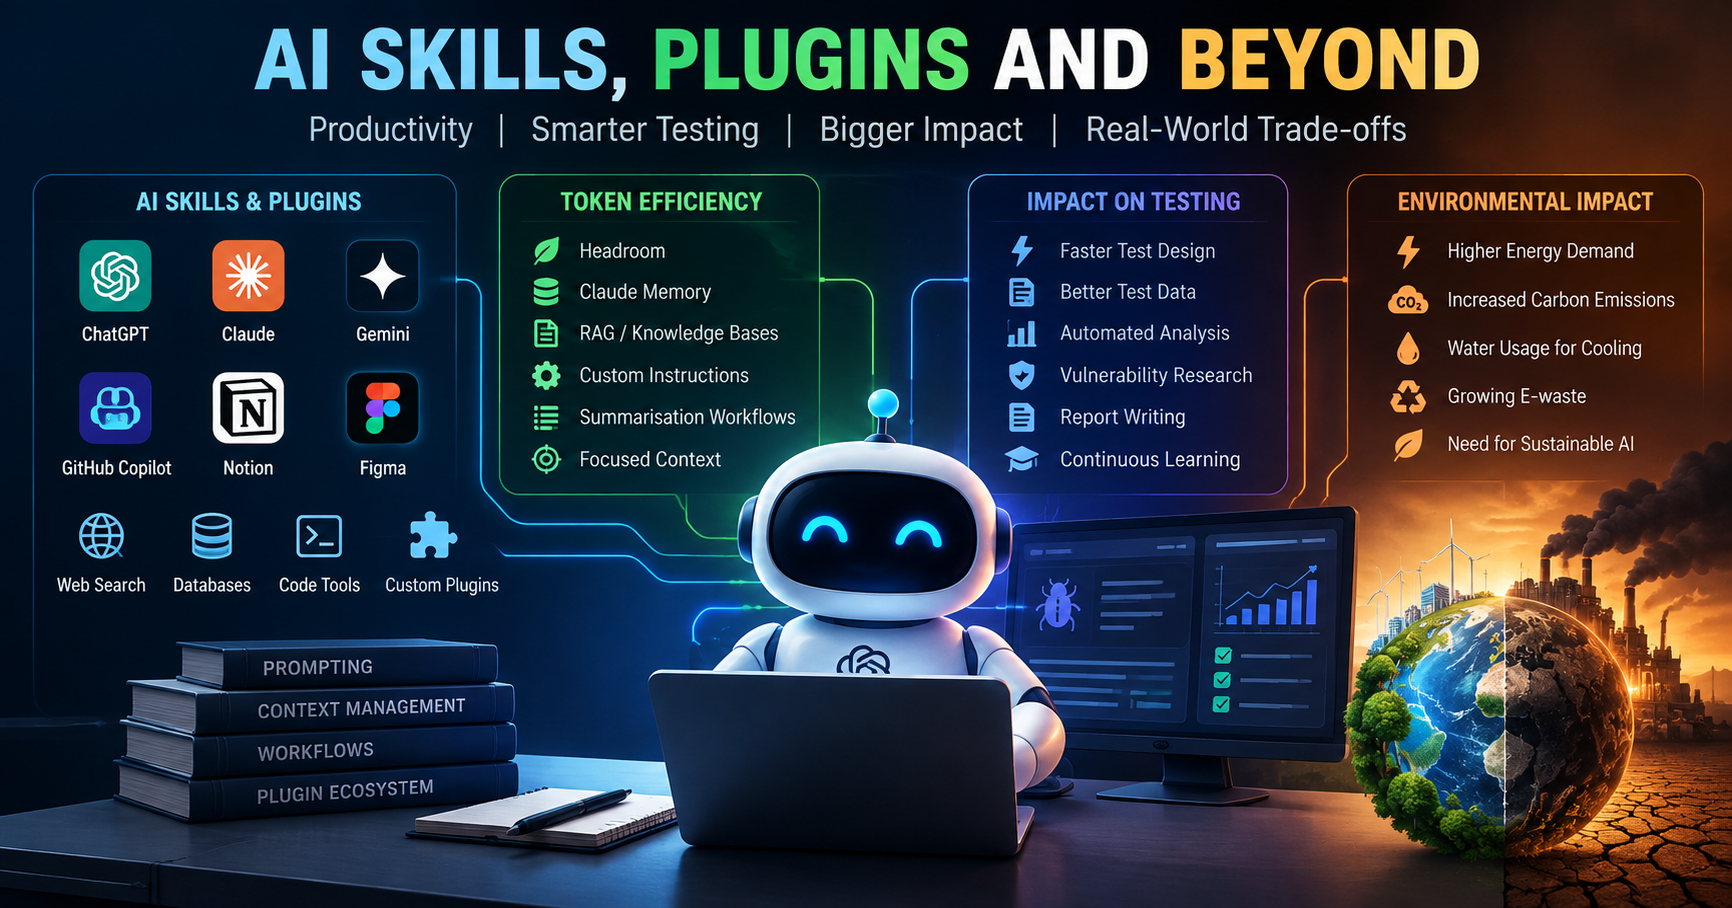
How AI skills, plugins, MCP, subagents, hooks, memory, and project instructions work together to turn a general-purpose model into a practical execution system.
How response manipulation works in web and mobile testing, why it succeeds, how to test for it with Burp Suite, how to rate it, and how to fix the root cause on the server.
Why security testing and compliance matter: types of security testing, PCI DSS and PCI SSF, and the OWASP Top 10.
Walkthrough of the TryHackMe Avengers Blog room: cookie and HTTP header inspection, FTP enumeration, directory brute-forcing, SQL injection login bypass and command injection.